Policy-Based Routing (PBR)
When a packet (encapsulated in a layer-2 frame) arrives at a router, the router data plane takes several steps to process the packet.
- The router checks the FCS and discards the frame if an error occurred in transmission.
- If FCS check passes, the router discards the frame header and trailer, leaving the layer 3 packet.
- Finally, the router does the equivalent of comparing the destination IP of the packet with the routing table, matching the longest-prefix route.
PBR overrides this destination-based forwarding logic. PBR intercepts the packet after deencapsulation on the incoming interface and before performing the CEF lookup. The decision making can be based on source IP address, type of traffic (www, ftp),…
                                                              +------> Gig0/1
----Frame--->.Gig0/0.---> PBR on Gig0/0 ---->Routing Table--->|------> Gig0/2
                                                              +------> Gig0/3
Why on the incoming interface? Because if we set PBR on outgoing interface, it means that the decision is already made according to the routing table.
Configuration Example
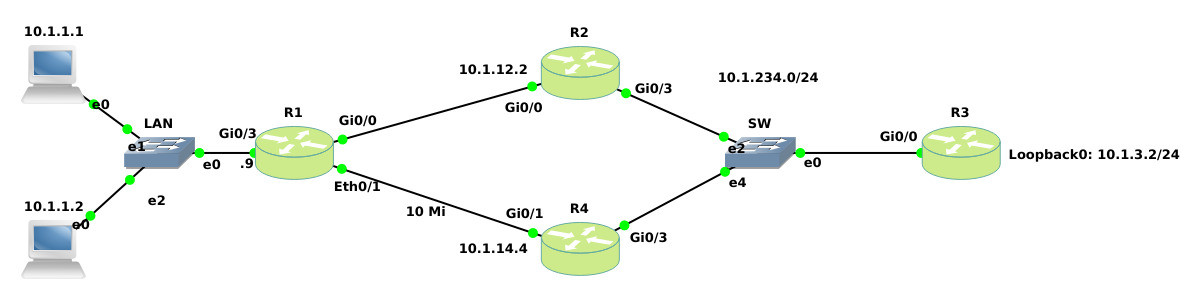
Base Configuration:
R1:hostname R1 interface GigabitEthernet0/0 ip address 10.1.12.1 255.255.255.0 ! interface GigabitEthernet0/1 ip address 10.1.14.1 255.255.255.0 speed 10 ! interface GigabitEthernet0/3 ip address 10.1.1.9 255.255.255.0 ! router eigrp R1 ! address-family ipv4 unicast autonomous-system 1 ! topology base exit-af-topology network 0.0.0.0 exit-address-family !R2:
hostname R2
!
interface GigabitEthernet0/0
 ip address 10.1.12.2 255.255.255.0
!
interface GigabitEthernet0/3
 ip address 10.1.234.2 255.255.255.0
!
router eigrp R2
 !
 address-family ipv4 unicast autonomous-system 1
  !
  topology base
  exit-af-topology
  network 0.0.0.0
 exit-address-family
R3:
hostname R3
interface Loopback0
 ip address 10.1.3.2 255.255.255.0
!
interface GigabitEthernet0/0
 ip address 10.1.234.3 255.255.255.0
!
router eigrp R3
 !
 address-family ipv4 unicast autonomous-system 1
  !
  topology base
  exit-af-topology
  network 0.0.0.0
 exit-address-family
R4:
hostname R4
!
interface GigabitEthernet0/1
 ip address 10.1.14.4 255.255.255.0
!
interface GigabitEthernet0/3
 ip address 10.1.234.4 255.255.255.0
!
router eigrp R4
 !
 address-family ipv4 unicast autonomous-system 1
  !
  topology base
  exit-af-topology
  network 0.0.0.0
 exit-address-family
In this case R1 chooses the upper route to reach the subnet on the right because it has 1 Gbps bandwidth as compared with the lower link (10 Mbps).
So PC2 (10.1.1.2) will be routed through the upper route to the subnet on the right.PC2> trace 10.1.3.2 trace to 10.1.3.2, 8 hops max, press Ctrl+C to stop 1 10.1.1.9 3.714 ms 2.326 ms 2.151 ms 2 10.1.12.2 4.961 ms 3.417 ms 6.650 ms 3 *10.1.234.3 7.818 ms (ICMP type:3, code:3)Now, we want to route the packets originating from PC2 (10.1.1.2) to be routed from the lower path.
R1(config)#interface gigabitEthernet 0/3
R1(config-if)#ip policy route-map PC2-over-low-route
R1(config)#route-map PC2-over-low-route permit
R1(config-route-map)#match ip address 101
R1(config-route-map)#set ip next-hop 10.1.14.4
R1(config-route-map)#exit
R1(config)#access-list 101 permit ip host 10.1.1.2 10.1.3.0 0.0.0.255
To verify:
PC2> trace 10.1.3.2
trace to 10.1.3.2, 8 hops max, press Ctrl+C to stop
 1   10.1.1.9   2.119 ms  2.926 ms  2.796 ms
 2   10.1.14.4   6.041 ms  6.047 ms  6.022 ms
 3   *10.1.234.3   9.844 ms (ICMP type:3, code:3)
R1#show route-map
route-map PC2-over-low-route, permit, sequence 10
  Match clauses:
    ip address (access-lists): 101
  Set clauses:
    ip next-hop 10.1.14.4
  Policy routing matches: 9 packets, 954 bytes

R1#show ip policy
Interface      Route map
Gi0/3          PC2-over-low-route
Above, we worked on traffic which enters a router, but it might be useful to use PBR to process packets generated by the router itself. However we used ip policy route-map at the interface level to handle this task. To make our IOS process locally created packets using PBR logic, configure ip local policy route-map name global command, referring to the PBR route map at the end of command. For example, IP SLA causes a router to create packets, so applying PBR to such packets can influence the path taken by the packet.