EIGRP Named Configuration Approach Example
ccnp-routing
Configure EIGRP for IPv4 and IPv6 with the named approach, compare it with a traditional configuration, and verify neighbors, topology, and authentication.
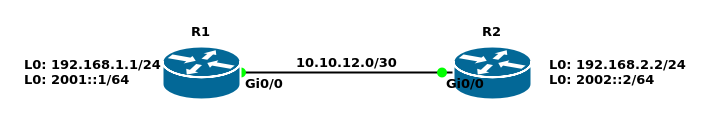
- Requirements:
- All interfaces should participate in EIGRP for IPv4 AS 1.
- All interfaces should participate in EIGRP for IPv6 AS 2.
- The variance option should be set to 2 for both autonomous systems.
- The Hello Interval should be set to 2 seconds for EIGRP for IPv4 AS1.
- The Hold Time should be set to 10 seconds for EIGRP for IPv4 AS1.
R1(config)#router eigrp R1
R1(config-router)#address-family ipv4 unicast autonomous-system 1
R1(config-router-af)#network 0.0.0.0
R1(config-router-af)#af-interface default
R1(config-router-af-interface)#hello-interval 2
R1(config-router-af-interface)#hold-time 10
R1(config-router-af-interface)#passive-interface
R1(config-router-af-interface)#exit-af-interface
R1(config-router-af)#af-interface gigabitEthernet 0/0
R1(config-router-af-interface)#no passive-interface
R1(config-router-af-interface)#exit-af-interface
R1(config-router-af)#topology base
R1(config-router-af-topology)#variance 2
R1(config-router-af-topology)#exit-af-topology
R1(config-router-af)#exit-address-family
R1(config-router)#address-family ipv6 unicast autonomous-system 2
R1(config-router-af)#topology base
R1(config-router-af-topology)#variance 2
R1(config-router-af-topology)#exit-af-topology
R1(config-router-af)#exit-address-family
R2(config)#router eigrp 2
R2(config-router)#variance 2
R2(config-router)#network 0.0.0.0
R2(config-router)#passive-interface default
R2(config-router)#no passive-interface gigabitEthernet 0/0
R2(config)#ipv6 router eigrp 2
R2(config-rtr)#variance 2
R2(config)#interface loopback 0
R2(config-if)#ipv6 eigrp 2
R2(config)#interface gigabitEthernet 0/0
R2(config-if)#ip hello-interval eigrp 1 2
R2(config-if)#ip hold-time eigrp 1 10
R2(config-if)#ipv6 eigrp 2
Verification on R1
R1#show ip route eigrp
Gateway of last resort is not set

D     192.168.2.0/24 [90/2570240] via 10.10.12.2, 00:00:22, GigabitEthernet0/0
R1#show ipv6 route eigrp
IPv6 Routing Table - default - 4 entries
D   2002::/64 [90/2570240]
     via FE80::26F:C8FF:FE76:5600, GigabitEthernet0/0
R1#show ip eigrp neighbors
EIGRP-IPv4 VR(R1) Address-Family Neighbors for AS(1)
H   Address                 Interface              Hold Uptime   SRTT   RTO  Q  Seq
                                                   (sec)         (ms)       Cnt Num
0   10.10.12.2              Gi0/0                     8 00:01:29    9   100  0  5
- Smooth round-trip time (SRTT): The number of milliseconds it takes for an EIGRP packet to be sent to this neighbor and for the local router to receive an acknowledgment of that packet.
- Retransmission timeout (RTO), in milliseconds: The amount of time that the software waits before retransmitting a packet from the retransmission queue to a neighbor
- Q Count: The number of EIGRP packets (Update, Query, and Reply) that the software is waiting to send.
R1#show ipv6 eigrp neighbors
EIGRP-IPv6 VR(R1) Address-Family Neighbors for AS(2)
H   Address                 Interface              Hold Uptime   SRTT   RTO  Q  Seq
                                                 (sec)         (ms)       Cnt Num
0   Link-local address:     Gi0/0                    13 00:07:01    6   100  0  3
  FE80::26F:C8FF:FE76:5600
R1#show ip eigrp topology
EIGRP-IPv4 VR(R1) Topology Table for AS(1)/ID(192.168.1.1)
Codes: P - Passive, A - Active, U - Update, Q - Query, R - Reply,
       r - reply Status, s - sia Status

P 192.168.2.0/24, 1 successors, FD is 328990720
        via 10.10.12.2 (328990720/327761920), GigabitEthernet0/0
P 10.10.12.0/30, 1 successors, FD is 1310720
        via Connected, GigabitEthernet0/0
P 192.168.1.0/24, 1 successors, FD is 163840
        via Connected, Loopback0
R1#show ipv6 eigrp topology
EIGRP-IPv6 VR(R1) Topology Table for AS(2)/ID(192.168.1.1)
Codes: P - Passive, A - Active, U - Update, Q - Query, R - Reply,
       r - reply Status, s - sia Status

P 2001::/64, 1 successors, FD is 163840
        via Connected, Loopback0
P 2002::/64, 1 successors, FD is 328990720
        via FE80::26F:C8FF:FE76:5600 (328990720/327761920), GigabitEthernet0/0
R1#show ipv6 interface loopback 0
EIGRP-IPv6 VR(R1) Address-Family Interfaces for AS(2)
                              Xmit Queue   PeerQ        Mean   Pacing Time   Multicast    Pending
Interface              Peers  Un/Reliable  Un/Reliable  SRTT   Un/Reliable   Flow Timer   Routes
Gi0/0                    1        0/0       0/0           6       0/0           50           0
Lo0                      0        0/0       0/0           0       0/0            0           0
R1#show ipv6 interface loopback 0
Loopback0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::26F:C8FF:FEF9:700
  No Virtual link-local address(es):
  Global unicast address(es):
    2001::1, subnet is 2001::/64
  Joined group address(es):
    FF02::1
    FF02::2
    FF02::A
    FF02::1:FF00:1
    FF02::1:FFF9:700
  MTU is 1514 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is not supported
  ND reachable time is 30000 milliseconds (using 30000)
  ND advertised reachable time is 0 (unspecified)
  ND advertised retransmit interval is 0 (unspecified)
  ND router advertisements live for 1800 seconds
  ND advertised default router preference is Medium
  ND RAs are suppressed (periodic)
  Hosts use stateless autoconfig for addresses.
EIGRP Message Authentication
R1 Configuration (Named Approach)R1(config)#router eigrp R1 R1(config-router)#address-family ipv4 unicast autonomous-system 1 R1(config-router-af)#af-interface gigabitEthernet 0/0 R1(config-router-af-interface)#authentication key-chain KC-EIGRP R1(config-router-af-interface)#authentication mode ? hmac-sha-256 HMAC-SHA-256 Authentication md5 Keyed message digest R1(config-router-af-interface)#authentication mode md5 *Dec 14 00:17:43.124: %DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 10.10.12.2 (GigabitEthernet0/0) is down: authentication mode changed R1(config-router-af-interface)#exit-af-interface R1(config-router-af)#exit-address-family R1(config-router)#exit R1(config)#key chain KC-EIGRP R1(config-keychain)#key 1 R1(config-keychain-key)#key-string VALUE R1(config-keychain-key)#cryptographic-algorithm md5 R1(config-keychain-key)#exit R1(config-keychain)#exitR2 Configuration (Traditional Approach)
R2(config)#key chain KC-EIGRP
R2(config-keychain)#key 1
R2(config-keychain-key)#key-string VALUE
R2(config-keychain-key)#cryptographic-algorithm md5
R2(config-keychain-key)#exit
R2(config-keychain)#exit
R2(config)#interface gigabitEthernet 0/0
R2(config-if)#ip authentication key-chain eigrp 1 KC-EIGRP
R2(config-if)#ip authentication mode eigrp 1 ?
  md5  Keyed message digest
R2(config-if)#ip authentication mode eigrp 1 md5
*Dec 14 00:41:17.148: %DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 10.10.12.1 (GigabitEthernet0/0) is up: new adjacency
Verification
R1#show ip eigrp 1 interfaces detail gigabitEthernet 0/0
EIGRP-IPv4 VR(R1) Address-Family Interfaces for AS(1)
                              Xmit Queue   PeerQ        Mean   Pacing Time   Multicast    Pending
Interface              Peers  Un/Reliable  Un/Reliable  SRTT   Un/Reliable   Flow Timer   Routes
Gi0/0                    1        0/0       0/0        1604       0/0         8016           0
  Hello-interval is 2, Hold-time is 10
  Split-horizon is enabled
  Next xmit serial
  Packetized sent/expedited: 5/1
  Hello's sent/expedited: 3046/4
  Un/reliable mcasts: 0/6  Un/reliable ucasts: 6/6
  Mcast exceptions: 0  CR packets: 0  ACKs suppressed: 0
  Retransmissions sent: 3  Out-of-sequence rcvd: 1
  Topology-ids on interface - 0
  Authentication mode is md5,  key-chain is "KC-EIGRP"
  Topologies advertised on this interface:  base
  Topologies not advertised on this interface: